

Strengthen your business' holiday cybersecurity with 24/7 monitoring, incident response planning, secure backups, and employee awareness.

November 11, 2026
Most business continuity plans fail at the same quiet points long before a real crisis ever hits. Knowing where these breakdowns happen lets you fix them before they become expensive problems.
A business continuity plan rarely fails all at once. It fails in small ways first: a phone number that no longer connects, a step nobody rehearsed, a vendor nobody double-checked. Those gaps sit quietly until a real disruption forces them into the open.
On paper, a plan can look airtight, listing every procedure and contact in neat order. Whether it holds up depends entirely on what happens when a disruption actually hits, and that's usually the moment teams discover the weak spots they had no chance to fix in advance.
At its core, a business continuity plan exists to keep a business running through events like cyberattacks or natural disasters, protecting critical functions and speeding recovery so downtime stays short and operations stay dependable. Delivering on that promise means finding the places where the plan can quietly give way, since that's where both the hidden risk and the real opportunity to strengthen it live.

Checking every box on a continuity plan can create a false sense of security, because the oversights that matter most rarely look urgent until a disruption drags them into view.
Outdated contact information is a common starting point: when a team can't reach the right people fast, even a minor outage stretches out longer than it should. A related failure shows up when the plan never catches up with changes in the business itself, whether that's new software or a shift in the supply chain, and each unaddressed change adds another layer to the gap.
Left unchecked, these small gaps compound until a manageable incident turns into a genuine crisis. Regular review is what catches weak spots while they're still small enough to fix.
Most plans share a handful of points where they're most likely to give way before they're ever truly tested, and these aren't the obvious errors but the quiet failures working behind the scenes.
An aging business impact analysis stops reflecting how the business actually runs today. Once staff, technology, or core functions shift, the BIA drifts out of sync, and the recovery strategies built on it stop matching what the business really needs.
Confusion sets in fast when people aren't sure what they're supposed to do mid-disruption. Without clearly assigned tasks, teams hesitate or duplicate effort, and that wasted motion costs time nobody can spare.
A communication plan missing key contacts or failing to account for different scenarios breaks down just as fast. Once a team can't reach each other or outside partners, even a well-designed recovery strategy stalls out.
Dependencies like third-party vendors or essential software are easy to leave out of a plan. If the supply chain isn't mapped in, a single missing link is enough to stop recovery in its tracks.
Skip regular testing, and there's no real way to know whether the plan works at all. At that point, continuity rests on hope rather than proof, and hope won't keep a business running through an actual disruption.
Running a test does more than satisfy a checklist; it's the clearest way to see how a team behaves under pressure and to surface problems that stayed hidden until then.
A single test run might show that certain steps take longer than planned or that some team members aren't clear on their role at all. It might also reveal that a backup system doesn't perform as expected, or that a key vendor can't actually deliver mid-crisis.
Each of those discoveries is a chance to fix the issue before it causes real damage. In Texas, where storms and outages can arrive with little warning, that kind of regular testing carries extra weight, and the lessons from each round make the plan sharper and the business more resilient.

Continuity planning can slide into a once-a-year habit, updated out of obligation and otherwise forgotten, and that routine is exactly what lets real risk hide in plain sight.
Once planning becomes a checklist, teams stop asking the hard questions that actually test the plan's logic. Some lean on a business continuity plan template without adapting it to their own operations, and with each passing cycle, the plan drifts further from how the business actually works.
For a plan that hasn't been examined closely in a while, the right question is simple: when was the contact list last updated, or the recovery time objectives (RTO) last tested? Details that small are often what decide how a crisis response actually plays out.

The warning signs are often subtle enough to miss entirely. Watch for these signals that recovery strategies may not hold up under real pressure:
Surviving a disaster is only part of what a business continuity plan is for; just as much is riding on reputation, relationships, and the bottom line, since clients and partners expect commitments to hold even when things go wrong.
When the plan fails, the damage goes well beyond downtime. Trust erodes, deadlines slip, and the business can carry that damage long after the disruption ends, which is exactly why finding and fixing the quiet breakdown points matters before they turn into real problems.
Overlooking the subtle points where a plan can fail amounts to betting that nothing will go wrong, and disruptions don't wait around for that bet to pay off. They find every weakness, no matter how small, and expose it on their own schedule.
The businesses that take the time to find and fix these hidden breakdowns ahead of time are the ones that recover fastest afterward. They don't just come through the disruption; they hold onto their reputation and their clients while doing it.
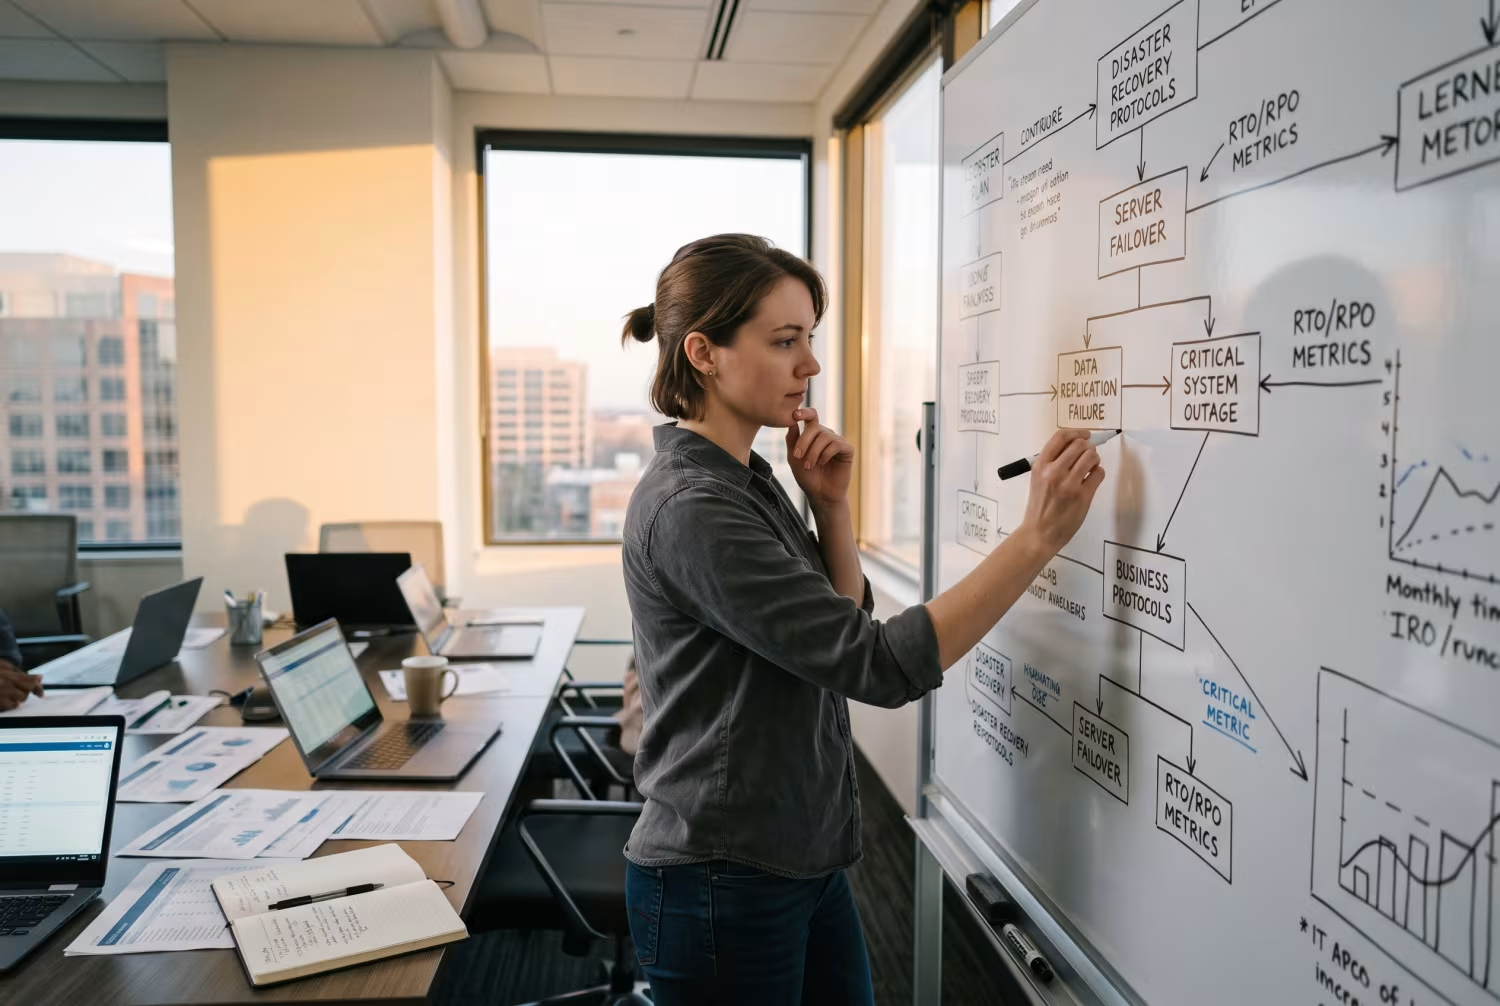
Many businesses with 15 to 70 users have a continuity plan that looks good on paper but may not stand up to a real crisis. At Allied IT Systems, we understand how easy it is for small details to slip through the cracks.
If you want to see how we approach finding and fixing these hidden risks, we invite you to start a conversation about your own setup. Our team is ready to help you strengthen your plan where it matters most.
If you find a lower price for the same level of service anywhere else, we’ll match it—no negotiation required. This offer is available to all qualified businesses.
[.mspl-button-text]Request a price match[.mspl-button-text]
Continuity plans deserve a review at least once a year, and sooner whenever a major change hits the business, including shifts in staff, technology, or critical functions. Regular updates are what keep the plan matched to how the business actually operates.
A business continuity plan covers how a business keeps running through any disruption, IT-related or not. Disaster recovery focuses specifically on restoring IT systems and data after an event, making it narrower in scope than a full BCP.
Testing is the only reliable way to confirm a plan works in practice rather than just on paper. It surfaces gaps, unclear instructions, or missing resources before a real disruption forces the issue, replacing assumptions with actual evidence.
A reliable communication plan depends on current contact information and backup methods for reaching key people when the primary channel fails. Practicing the plan during tests keeps everyone clear on their role, cutting down on confusion when every minute counts.
A plan built for supply chain disruption needs backup vendors and alternative processes for critical supplies identified in advance. Mapping out dependencies and keeping a ready list of contacts makes it possible to act quickly and keep operations moving.

Tommy Fauth is a technology and cybersecurity executive with over 20 years of experience in enterprise IT, managed services, infrastructure, and regulatory compliance. A Marine Corps veteran, he helps organizations improve security, reliability, and business performance through practical technology leadership.